Your next release. One step ahead.
Catch security issues and store rejection risks before you submit. Your extension, checked from the terminal you already use.
npx @extenshi/cli@latest review ./dist.zipNode 20+ · Review is free without an account
$working together
Chrome · Firefox · Edge
 Review-risk runs locally
No account required
Review and scan your build
Run policy and browser compatibility checks locally. Use your API key to submit a build for security scanning.
npx @extenshi/cli review ./dist.zipFree · runs locally
Flags rejections, slow-review triggers, and auto-disable risks before you submit.
Diffs against your last published manifest with --extension-id.
npx @extenshi/cli advise ./dist.zipFree · runs locally
Finds code that recent Chrome, Edge and Firefox releases break or change, with the file and line.
Every change it checks is listed on cli.extenshi.io/changes.
npx @extenshi/cli scan ./dist.zipThe deep scan
Uploads the packaged build to Extenshi for server-side analysis.
Live per-scanner progress, then an HTML report opens in your browser.
A report you can actually read
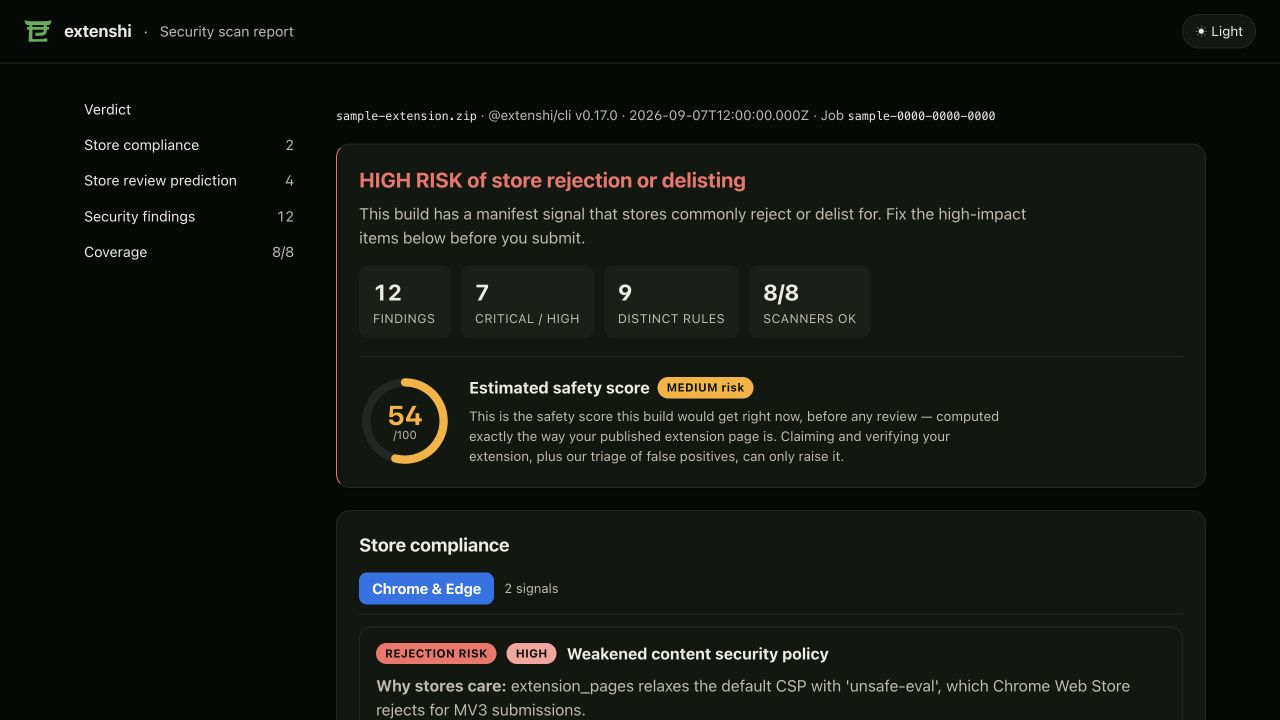
Every extenshi scan opens an HTML report in your browser by default — or pass --json / --format stdout for pipelines and the terminal.
A catalog-style safety score
See the verdict, finding counts and estimated safety score together. This sample scores 54/100.
Actual CLI output with sample data for a fictional extension.
Eight scanners on every build
The same engine behind our public catalog runs against your artifact — findings by severity.
- Manifest & permission analysis
- Code vulnerability analysis
- Cryptocurrency & wallet abuse
- Behavioral & obfuscation analysis
- Network endpoint & exfiltration analysis
- Obfuscation & evasion detection
- Malware signature matching
- Known-vulnerable dependency detection
Block releases with critical findings
Run a scan in GitHub Actions and use jq to fail the job when the report contains a critical finding.
- name: Scan and gate
  env:
    EXTENSHI_API_KEY: ${{ secrets.EXTENSHI_API_KEY }}
  run: |
    npx -y @extenshi/cli@latest scan ./dist.zip --json > scan.json
    jq -e 'all(.scanners[].findings[]?; (.severity | ascii_upcase) != "CRITICAL")' scan.json
--json for machine output
Parse findings in your pipeline and gate on severity counts.
CI-timeout preflight built in
A fast probe detects short CI outbound timeouts before the real scan.
Auto-refund on failure
If a scan dies mid-stream, the credit is refunded within a minute.
Free to start
3 free scans, one-time on any build. review is always free. Need more? Buy prepaid credit packs that never expire.
Buy credit packsOne API key works across the CLI and MCP. No subscription — top up scans and reads whenever you need them.
Chrome Web Store questions, answered
- Will it tell me why the Chrome Web Store would reject my extension?
- That is what review is for. It predicts what will likely be rejected, what triggers a slow manual review, and what would auto-disable the extension for existing users on update. Every finding names the Chrome Web Store program policy it predicts against, so you can read the rule at the source and quote it if a reviewer disagrees.
- Does my code get uploaded anywhere?
- Your build never leaves your machine with review: it reads the manifest and listing text inside the package locally, and needs no API key. Two things do go out, neither of them your code. Passing --extension-id fetches your last published manifest from our catalog so it can diff for auto-disable risk — that sends the extension id, not your build. And the CLI reports anonymous usage (command and flag names, versions, a coarse error kind — never file paths, artifact contents or manifest data), which you can turn off with DO_NOT_TRACK=1 or EXTENSHI_TELEMETRY=0. scan is the one command that does upload the packaged artifact, because the eight-scanner engine runs server-side.
- Do I need an account or an API key?
- Run review locally without an account. For scan, sign in with npx @extenshi/cli login to get an API key. Every account includes a one-time free allowance of 3 scans and 10 reads, with no card required.
- Does it check Manifest V3 compliance?
- Yes. The review rules read your manifest directly, so Manifest V3 problems — permissions you declare but never use, broad host access like <all_urls>, and permission additions that would auto-disable your extension for existing users — are flagged before you submit rather than after a reviewer finds them.
- Which stores does it cover?
- Chrome Web Store, Firefox Add-ons, and Edge Add-ons. Permission sets differ per store, so review takes --store chrome|firefox|edge and diffs the manifest against the right one; the scan report splits store-compliance findings into the Chrome/Edge and Firefox sections you actually publish to.
- Does it check my store listing too, or only the code?
- Both. Moderation reads your listing as closely as your code, so the listing rules run on every invocation using the name and short description from the package — including each locale you ship. The full description only exists in the developer dashboard, so pass it with --listing to have the keyword-spam rules read that as well.
- Can I run it in CI and fail the build on findings?
- Yes. Run it with --json in GitHub Actions and gate on the severity counts you care about. Note that the exit code signals whether the scan ran, not whether it found anything — a scan that completes with critical findings still exits 0, so read the JSON and decide the threshold yourself. A pre-flight probe detects short CI outbound timeouts before the real scan starts.
- What does it cost?
- review is always free. Scanning draws on a one-time free allowance of 3 scans per account, on any build — no ownership claim needed. Beyond that you buy prepaid scan packs — no subscription, and the credits never expire. A scan that dies mid-stream is refunded automatically within a minute.
More developer tools
MCP server
The cross-store catalog and scanner, inside your AI tools.
Manifest generator
Build an MV3 manifest with live store-policy checks.
Pin guide
Illustrated steps that get your extension pinned to the toolbar.
Uninstall feedback
A hosted exit survey — find out why users leave.
Policy generator
A store-ready privacy policy from your permissions.
Icon generator
Draw with your agent, verify in real toolbar mockups.
Monetize
A paywall inside your extension, paid out to your own Stripe account.
Check your build before you submit
Start with a local policy review. Add a security scan when your build is ready.
npx @extenshi/cli@latest review ./dist.zip